Crime story: How North Korea Gets Its IT Workers Hired at American Companies
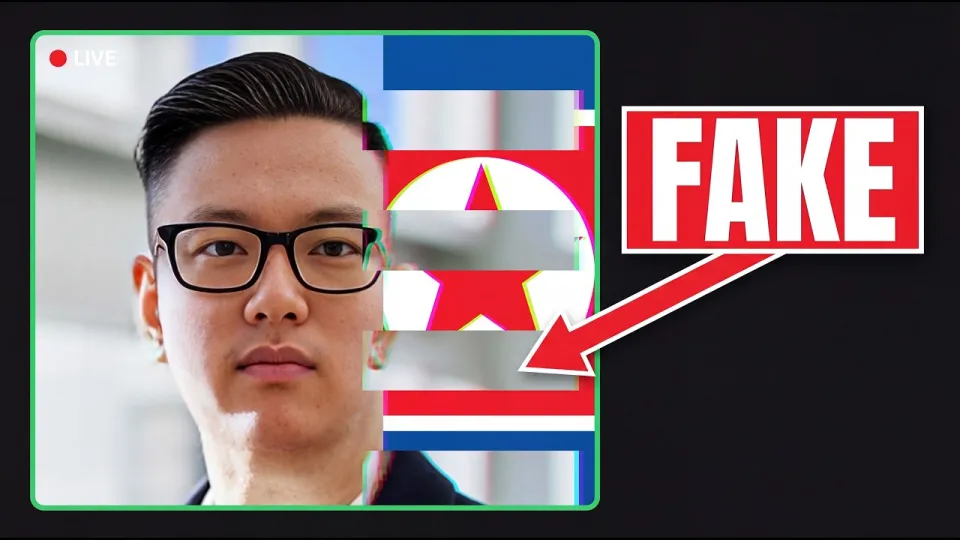
Video: Company Has No Idea Its New Hire Is a North Korean Hacker (crime story)
· based on the channel Max Crime
Key takeaways
- KnowBe4, a security-awareness firm, hired a North Korean IT worker who passed four video interviews and a background check before malware appeared on his work laptop.
- Christina Chapman of Arizona kept more than 90 laptops on wire shelves in her home, each tagged with a company and a stolen American name.
- Chapman was sentenced to 102 months in federal prison in July 2025; she kept about $177,000 while more than $17 million moved through her house.
- The FBI's IC3 issued a public service announcement in January 2025 on North Korean IT workers infiltrating US companies.
- Microsoft tracks the scheme as 'Jasper Sleet'; the group is also known as Famous Chollima.
A North Korean IT worker is hired by an American company when a stolen or borrowed US identity, an AI-altered photo and a convincing video interview get a real person through the hiring process — and then a laptop shipped to an American address carries the intruder onto the corporate network. The scheme is not a hack of the company's defenses; it is a payroll fraud and an insider threat dressed as a new hire. The most striking documented case is KnowBe4, a Florida company whose entire business is training employees to spot social engineering, which discovered in 2024 that the software engineer it had just hired was operating from North Korea.
What the KnowBe4 case shows about a fake IT worker
KnowBe4 hired a purported software engineer who cleared four video interviews, a clean background check and a photo that turned out to be AI-altered. The company's own account, published in July 2024, describes how the deception unraveled within days: the work laptop was flagged by the security team, and the activity looked like malware loading rather than normal setup. The applicant had used a real American's name and a stolen identity, and the interview process had been conducted remotely, with the candidate's camera feed and answers convincing enough to move through successive rounds. The lesson is structural rather than embarrassing: remote hiring pipelines verify documents and voices, not physical presence, and a determined impersonator can satisfy every checkbox a typical HR department uses.
The laptop farm: 90 machines on wire shelves in Arizona
The infrastructure that makes these hires possible is a laptop farm — a house full of company-issued computers connected to American residential internet, each one a remote doorway for a worker sitting thousands of miles away. Christina Chapman, an American citizen living in Arizona, kept more than ninety laptops on wire shelves in her home, each tagged with the name of a company and the stolen identity assigned to it. She ran this operation for years, receiving the machines, keeping them powered and connected, and forwarding access to the overseas workers. Prosecutors said the scheme generated more than $17 million in revenue for the broader network; Chapman herself kept about $177,000. She was sentenced to 102 months in federal prison in July 2025. Her defense was that she did not know who she was really working for; prosecutors pointed to her own messages as evidence she did.
How the scheme works, step by step
- Identity acquisition: the network buys or steals the personal data of real US residents, sometimes including photos, diplomas and references.
- Application: the worker applies for remote software, cloud or engineering roles using that identity, often with an AI-altered headshot and a polished résumé.
- Interviews: video calls are handled by a fluent English speaker or with technical assistance off-camera, so the person on screen may not be the person who will do the work.
- Laptop logistics: the company ships hardware to a US address controlled by a facilitator like Chapman, who connects it to a residential network.
- Remote access: the overseas worker logs in through that connection, appearing to be an ordinary American employee, and begins exfiltrating data, planting malware or wiring wages abroad.
- Payroll: salaries are routed through US bank accounts opened with the stolen identities, then moved overseas.
Why background checks and video interviews fail
A background check confirms that a name, a Social Security number and an address belong together — not that the person on the call is that name. Video interviews test composure and English, both of which can be supplied by a hired stand-in or by someone reading prepared answers. The FBI's IC3 public service announcement in January 2025 warned companies directly about North Korean IT workers, noting that they often request remote positions, use false identities and rely on third-party facilitators to host company equipment. Microsoft tracks the broader activity as "Jasper Sleet," a cluster tied to the North Korean state, and the group is also known as Famous Chollima. The money matters: US authorities say the wages and extorted ransoms fund the country's weapons programs, which is why the scheme is treated as a national-security matter and not just HR fraud.
The night of the alert: what a compromise looks like from inside
A compromise usually surfaces not in an interview room but on a security console, when a newly issued laptop begins behaving like a machine that is already occupied. In the KnowBe4 incident, the internal alert came within days of the laptop being set up, and the pattern resembled malware staging rather than a new employee installing tools. From there the response is forensic: isolate the device, review what was accessed, check whether credentials were harvested, and notify law enforcement. The uncomfortable detail is timing — the intruder had already been inside the perimeter, with a valid badge and a valid paycheck, before any technical control fired. Companies that catch these hires early usually credit anomaly detection on endpoints, not the interview panel.
The questions companies and employees keep asking
Can a determined impersonator really pass four rounds of interviews? Yes — the KnowBe4 case is the proof, and it involved a company whose staff are professionally trained to detect deception. Does the facilitator always know who they are working for? Not according to Chapman, though prosecutors argued her messages showed otherwise; juries tend to weigh documentary evidence over later denials. Would a small business notice? Often not, because the warning signs are administrative: a candidate who insists on a specific shipping address, a résumé that cannot be verified by phone, a reluctance to appear in person, or a bank account name that does not quite match. The most effective countermeasures are unglamorous — in-person or verified-identity onboarding, shipping hardware only to verified addresses, monitoring for unusual log-in geography and treating every new remote hire as a potential insider for the first ninety days.
What the Chapman sentence signals
The 102-month sentence handed to Christina Chapman in July 2025 is a signal that US courts now treat laptop farming as serious criminal infrastructure rather than a gray-area work-from-home arrangement. More than $17 million moved through her house while she kept roughly $177,000, a ratio prosecutors used to argue she understood the scale of what she was enabling. The case also confirmed that the scheme has an American face by design: the DPRK IT worker program depends on US residents willing to host machines, lend addresses and open accounts. Enforcement has followed the facilitators as aggressively as the workers, and the FBI has said the practice is widespread across the country, not confined to one state.
Summary
The crime story of North Korean IT workers is a story about trust in hiring: a stolen name, an AI-touched photo and a laptop on an American shelf are enough to put a foreign operative on a company payroll. KnowBe4's experience shows that even security professionals can be fooled, while the Chapman case shows the physical layer — houses full of tagged laptops — that the scheme cannot function without. The channel Max Crime breaks down the full timeline, from the interviews to the FBI at the door, in its video investigation of the case.
Source: Company Has No Idea Its New Hire Is a North Korean Hacker (crime story) · Markdown version
Questions & answers
How did a North Korean IT worker get hired by a US company?
By using a stolen American identity, an AI-altered photo and a convincing remote interview process. The company shipped a work laptop to a US address controlled by a facilitator, who connected it to a residential network so the overseas worker could log in and appear to be a local employee.
What is a laptop farm?
A laptop farm is a location, often a private home, where company-issued computers are kept powered on and connected to American internet so remote workers abroad can access corporate networks through them. Christina Chapman kept more than ninety such machines on wire shelves in her Arizona home, each tagged with a company and a stolen name.
How much money is involved in these schemes?
Prosecutors said more than $17 million moved through Chapman's operation, while she personally kept about $177,000. The wages and related proceeds are believed to fund North Korea's weapons programs, which is why US authorities treat the cases as national security matters.
Can background checks stop fake remote hires?
Not on their own. A background check verifies that a name and documents exist, not that the person on a video call is that individual. Companies need verified-identity onboarding, hardware shipped only to confirmed addresses, and monitoring of new remote hires for unusual log-in behavior.